TL;DR

Get business pricing on tech for your team
- Business-only prices and quantity discounts
- Tax-exempt purchasing
- Multiple users, one account, clear invoices
A WIRED headline reports that a supply chain attack put malicious Anthropic Claude extensions on thousands of devices. The available material contains no article body, so the attack’s timing, mechanics, confirmed device count and response remain unverified.
The WIRED headline identifies the incident as a supply chain attack involving Claude extensions, but it does not say which extensions were affected, how they were distributed or who developed them. Without the article’s reporting or a detailed statement from Anthropic, those specifics cannot be independently established here.
The phrase “thousands of devices” appears in the WIRED headline, but no count, measurement period or counting method is provided. It should be treated as a reported scale, not as a verified tally of infected devices, affected users or successful compromises. No details are available about what the extensions did or whether they accessed user data.
The supplied material also does not identify when the attack was discovered, whether the extensions were removed, or what guidance Anthropic gave users. Those are central facts for assessing immediate risk and determining whether users need to take action.
Security briefing · Extension supply chain
Malicious Claude Extensions Reach Thousands of Devices
A WIRED headline reports a supply chain attack involving Anthropic Claude extensions. The article details supplied here do not establish the timing, delivery method, confirmed scale, or user impact.
01 / Incident at a glance
Known signal, missing details
The supplied information identifies the broad incident category and target. The facts needed to assess user risk remain unreported in the material available here.
A supply chain incident
The WIRED headline describes malicious Anthropic Claude extensions reaching devices through a supply chain attack.
Which extensions?
No extension names, publisher, marketplace, product version, or distribution channel are included.
What happened to users?
The available material does not establish what the code did, what it could access, or whether users experienced harm.
02 / How the risk can travel
Trust can be the entry point
Extensions add capabilities to AI tools, while bringing in software beyond the core product. A compromised delivery path can make unsafe code appear legitimate.
Extension is built
A publisher develops an add-on for a tool.
Trust path is targeted
A supply chain attack can target a trusted delivery step.
Users install
Users may believe the extension is legitimate.
Impact depends on access
Possible effects depend on code and permissions.
03 / Scope & evidence
“Thousands” needs a denominator
Without a count, time window, and counting method, the headline’s scale cannot be independently assessed from the supplied details.
04 / What would clarify risk
Evidence users need next
A fuller account from the original reporting or an official notice would help users determine whether they need to act.
Names and availability
Which extensions were affected, when they were available, and whether they have been disabled or removed.
Behavior and access
What the code did, what permissions it had, and whether investigators found data theft or other impact.
Count and method
How the device estimate was calculated, what it counts, and over what time period.
Response for users
How to check installations and what steps to take if an affected extension was used.
05 / Key questions
What remains unanswered
The headline raises a meaningful security concern, but the available detail is too limited to judge the incident’s severity.
How many devices were affected?
The headline says “thousands,” with no exact count, time window, or counting method in the supplied material.
What did the extensions do?
Their behavior, permissions, and any access to prompts, credentials, files, or other user data are not described.
Has Anthropic issued user guidance?
No response or instructions are included in the available material.
Risks Across Claude’s Extension Supply
Extensions can add features to AI tools, but they also introduce software from outside the core product. If malicious code enters an extension’s distribution path, users may install it while believing it is legitimate. The incident described in the WIRED headline therefore raises a practical question: how extensions are reviewed and distributed, and how quickly users can be warned when one is unsafe.
The consequences depend on what the extensions could access and do. The supplied material does not establish whether they collected prompts, credentials or files, or whether the reported devices experienced any harm. Until those details are confirmed, the headline signals a security concern but does not establish the extent of user impact.
Products Worth Considering

Bose QuietComfort Wireless Bluetooth Headphones with Active Noise Cancellation, Mic, USB‑C Charging, Deep Bass, 24‑Hour Battery – White Smok
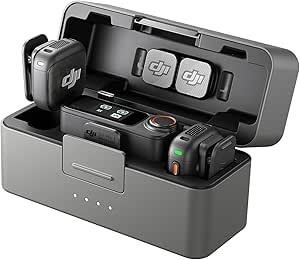
DJI Mic 3 Wireless Microphone System (2 Transmitters, 1 Receiver, Charging Case)

Amazon Kindle Scribe Colorsoft 64GB (1st Generation)
As an affiliate, we earn on qualifying purchases.
How Extension Attacks Can Spread
A supply chain attack targets a trusted part of the process that delivers software, rather than relying only on users to download an obviously suspicious program. In an extension incident, that could involve a compromised publisher account, development process or distribution channel. The WIRED headline does not specify which, if any, of these routes applied.
Claude extensions are the stated target, but no platform, extension marketplace or product version is identified in the supplied material. That makes it impossible to tell whether the issue affected a particular integration or a wider group of users. The WIRED headline is the only incident-specific detail provided.
Attack Scope Still Unverified
The supplied material does not establish which extensions were malicious, when they were available, how many devices were affected or what the code did. It also gives no information about data access, confirmed victims, the attacker’s identity or Anthropic’s response. The WIRED headline’s “thousands” figure has no stated baseline, time window or counting method, so the scope cannot be independently assessed from the details provided.
It is also unclear whether the headline describes confirmed installations, devices exposed to an extension, or devices where malicious activity was detected. Those categories can represent different levels of risk and should not be treated as interchangeable.
Details Needed for User Guidance
A fuller account from Anthropic or the original WIRED reporting would need to identify affected extensions and explain whether they were disabled or removed. Users would also need clear guidance on checking installations and on any steps to take if they used an affected extension.
Further reporting should clarify how the attack reached users, what evidence supports the device estimate and whether investigators found data theft or other impact. Until those details are available, the incident’s reported scale should be read cautiously.
Where I land
I view the incident reported in the WIRED headline as a meaningful warning about the risks that can enter through software extensions, but the details here are too limited to judge its severity. A reported device count without a method, named extensions or evidence of what the code did does not tell readers whether the main risk was exposure, data access or confirmed harm.
The strongest counterargument is that an attack reportedly reaching thousands of devices could represent substantial exposure even if the damage is not yet known. I would give the incident greater weight if detailed WIRED reporting or an Anthropic statement identified the extensions, documented their behavior and explained how the device estimate was calculated. Evidence of data access or confirmed user impact would change my assessment most.
Source: WIRED headline via Google News
Key Questions
What happened to Claude extensions?
A WIRED headline reports that a supply chain attack put malicious Anthropic Claude extensions on thousands of devices. The available material does not describe the affected extensions or attack method.
How many devices were affected?
The WIRED headline says “thousands,” but no exact count, time window or counting method is provided. The number cannot be independently verified from the details available here.
What did the malicious extensions do?
The available material does not say what the extensions did, what permissions they had or whether they accessed user data.
Has Anthropic issued instructions for users?
No response or user guidance is included in the available material. A fuller report or an official notice would be needed to establish recommended steps.
Source: Anthropic