TL;DR

Get business pricing on tech for your team
- Business-only prices and quantity discounts
- Tax-exempt purchasing
- Multiple users, one account, clear invoices
A Tom’s Hardware headline says a Windows malware payload can send stolen data to Claude to assess a victim’s assets, then delete itself. It also says the payload can switch models if one refuses or skip the AI step; details such as confirmed infections, scale and technical evidence are unavailable here.
Windows malware described in a Tom’s Hardware headline can send stolen data to Claude to rank a victim’s assets by value, a reported use of generative AI that could help attackers prioritize targets. The headline also says the payload can switch models if one refuses or skip the AI step, but the available account does not establish how widely it has been used or provide independent technical confirmation.
The reported workflow connects data theft with an assessment of what a victim may own or control. According to the headline, the malware supplies stolen information to Claude and uses the response to build a custom target assessment. That suggests an attempt to sort victims or their assets by perceived value, rather than treating every compromised system as equally attractive. The report does not specify what data is sent, what criteria the model applies or how the resulting ranking changes an attacker’s actions.
The headline says the malware can switch models if one refuses, and can also skip the AI step entirely. Those options indicate that the described operation is not wholly dependent on a successful response from one model. The account provided here does not identify alternative models, explain how a refusal is detected or say whether the fallback behavior has been observed in an actual infection.
It also says the payload deletes itself. That detail may complicate analysis after execution, but the supplied information does not describe what is deleted, whether other malware components remain, or whether investigators recovered a sample. No victim names, incident counts, dates, or evidence of confirmed data transfers are included in the available headline-only account.
Threat report · Windows malware · Evidence watch
AI-Assisted Malware Could Rank Stolen Assets
Tom’s Hardware reports that a Windows malware payload can send stolen data to Claude to assess a victim’s assets, then delete itself. The headline also describes model switching or skipping the AI step. The available account does not establish confirmed infections, scale, or independent technical evidence.
What the headline describes
The proposed sequence links data theft with a model-assisted estimate of which accounts, systems, or business assets may merit attention.
Collect
Information is taken from a compromised Windows environment, according to the report.
Assess
The headline says stolen data is sent to Claude to rank a victim’s assets by value.
Adapt
If one model refuses, the payload reportedly can switch models—or skip AI altogether.
Delete
The headline says the payload deletes itself; what is removed and how is unspecified.
Why defenders are watching
If accurate, the behavior could help attackers triage information already stolen. Its practical value depends on data quality, model output, and what an attacker does next.
Selective follow-up
An assessment might help sort accounts or systems by perceived value, rather than treating every compromised environment the same.
Not tied to one response
Model switching or bypassing AI could let the described workflow continue without a successful response from one service.
Protect and detect data
Limiting access to sensitive information and detecting unauthorized collection or transfer remain core responses.
The report describes a capability; prevalence, effectiveness, and confirmed victim impact remain unknown from the supplied information.
Known versus unknown
The headline provides a concise claim. Without the article body or a technical report, key operational details remain open.
| Topic | Available account says | Not established here |
|---|---|---|
| Model use | ✓ Stolen data may be sent to Claude to rank assets. | ~ Data fields, prompt, output, and handling of sensitive information. |
| Fallback | ✓ The payload may switch models or skip AI. | ~ Alternative models, refusal detection, and observed operation. |
| Self-deletion | ✓ The headline says the payload deletes itself. | ~ What is deleted, whether other components remain, and reliability. |
| Impact | — No victim names or infection counts are included. | ~ Scale, deployment timeline, affected sectors, and confirmed incidents. |
A headline can describe a capability seen in code, a test, or an incident. The supplied material does not say which, and it does not independently confirm data transfers to Claude.
What would clarify the story
Technical evidence and independent reporting could show whether the described behavior reached victims and what role the model played.
Sample and network analysis
Publish sample details and observed traffic, distinguishing implemented features from activity confirmed in victim environments.
Scope and response
Statements from Anthropic, affected organizations, or incident responders could clarify timeline, reach, and any confirmed model interaction.
Where the evidence lands
A model could help sort stolen information after a breach. The headline-only account does not show that the approach is widespread, effective, or materially different from manual review.
Worth tracking.
Not yet quantified.
The strongest case for concern is that even an experimental workflow could shorten the time needed to identify valuable accounts or systems in a large data set. Greater confidence would require a documented sample, verified model traffic, assessment output, and evidence connecting the behavior to confirmed incidents. Evidence that a ranking changed attacker actions would further clarify its impact.
Key questions
Answers from the supplied account are limited to what the headline states.
What does the malware reportedly do with Claude?
It sends stolen data to Claude to rank a victim’s assets by value. The data fields and a sample response are not provided.
Are organizations confirmed to be infected?
No victims or infection count are identified in the headline-only account, so the scale of deployment is not established.
Can it continue if a model refuses?
The headline says it can switch models or skip the AI step. The alternatives and fallback mechanics are unspecified.
What does “deletes itself” mean?
The headline says the payload deletes itself, but does not explain what is removed, whether other components remain, or how reliably it happens.
AI Could Shape Attacker Priorities
If the reported behavior is accurate, the notable change is the use of a language model as part of post-theft triage. Attackers could use information already collected from a compromised environment to estimate which accounts, systems or business assets merit further attention. That could make their follow-up choices more selective, though the headline alone does not show that the assessment produces accurate or useful rankings.
The claimed ability to change models or avoid AI also matters for defenders and service providers. It implies the workflow may continue when one model does not respond as desired. At the same time, a model’s involvement does not establish that it independently takes actions or that the malware is more effective than conventional methods. The operational impact depends on the stolen data, the prompt and the attacker’s decisions after receiving an assessment.
For organizations, the basic defensive priority remains preventing access to sensitive information and detecting its unauthorized collection or transfer. The report offers no evidence that model use replaces familiar intrusion techniques. It does, however, raise questions for incident responders about whether data leaving an environment could be used to generate targeted assessments through external AI services.
Products Worth Considering

Amazon Kindle Paperwhite Signature Edition (12th Generation, 2024), 32 GB, Metallic Black

Bose QuietComfort True Wireless Noise-Cancelling Earbuds, Black
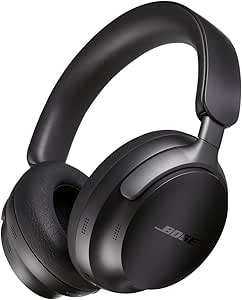
Bose QuietComfort Ultra Wireless Noise-Cancelling Headphones with Spatial Audio, Black
As an affiliate, we earn on qualifying purchases.
A Report With Limited Technical Detail
The supplied information is a headline from Tom’s Hardware referring to Anthropic, the company behind Claude. The article body was not available, so this account cannot include the underlying sample analysis, researcher findings, dates, or Anthropic’s full explanation. The headline describes an AI-assisted capability; it does not, by itself, establish the malware’s prevalence or verify that Claude processed data taken from real victims.
That distinction is material because a headline compresses technical qualifications. It may describe a capability observed in code, a test, or a reported incident, but the available text does not say which. There is also no information here about the malware’s distribution method, the industries or regions affected, or whether the model interaction was direct or routed through another service. These gaps limit what can be stated about the incident’s reach.
Scale and Model Use Unconfirmed
The available account leaves the malware sample and its evidence unspecified. It does not establish how many systems were affected, whether any named organization was compromised, or whether the reported behavior has been seen outside analysis or testing. It also provides no timeline for development, discovery or deployment.
How Claude was used remains unclear. The headline says stolen data is fed to the model to rank assets, but it does not identify the data fields, explain how sensitive information was handled, or provide the model’s output. It is not clear whether the model generated a recommendation that attackers reviewed or whether the process was automated. No direct quote or detailed statement from Anthropic is included in the supplied material.
The claimed fallback and self-deletion behavior also lack supporting detail here. Without the article body or a technical report, readers cannot determine what triggers a model switch, which other models may be used, what “deletes itself” refers to, or how reliably those functions work.
Technical Evidence Would Clarify Reach
The next useful development would be publication of the technical analysis behind the report: sample details, observed network behavior, and evidence distinguishing an implemented capability from activity confirmed in victim environments. That could establish whether data was actually sent to Claude and how the model’s assessment was used.
Further reporting or statements from Anthropic, affected organizations, or incident responders could clarify the timeline, scope and response. Until those details are available, the reported technique should be understood as a described malware capability, with its real-world prevalence and impact still unknown.
Where I land
I see this as a report about a plausible shift in how stolen information could be used: a model may help sort targets after a breach. That is worth tracking, but the headline-only evidence does not show that the method is widespread, effective, or materially different from an attacker manually reviewing the same data. The distinction between a capability in a sample and confirmed use against victims should remain clear.
The strongest counterargument is that even a limited or experimental workflow could reduce the time needed to identify valuable accounts or systems, especially when a victim’s data is extensive. I would give the claim more weight if a technical report documented the sample, verified model traffic, explained the assessment output, and connected those observations to confirmed incidents. Evidence that the model’s ranking changed attacker behavior would further alter my assessment.
Source: Anthropic
Key Questions
What does the reported malware do with Claude?
The headline says it sends stolen data to Claude to rank a victim’s assets by value. The available details do not explain the data fields or show a sample response.
Does the report confirm that organizations were infected?
The supplied headline-only account does not identify victims or give an infection count. It is not enough to establish the scale of real-world deployment.
Can the malware operate if an AI model refuses?
The headline says it can switch models if one refuses or skip the AI step. It does not identify the alternative models or explain how those fallback paths work.
What does self-deletion mean in this report?
The headline says the payload deletes itself, but the available account does not specify which files or components are removed, or whether other parts of an infection remain.
Source: Anthropic