By Thorsten Meyer | November 2, 2026 | ThorstenMeyerAI.com

Get business pricing on tech for your team
- Business-only prices and quantity discounts
- Tax-exempt purchasing
- Multiple users, one account, clear invoices
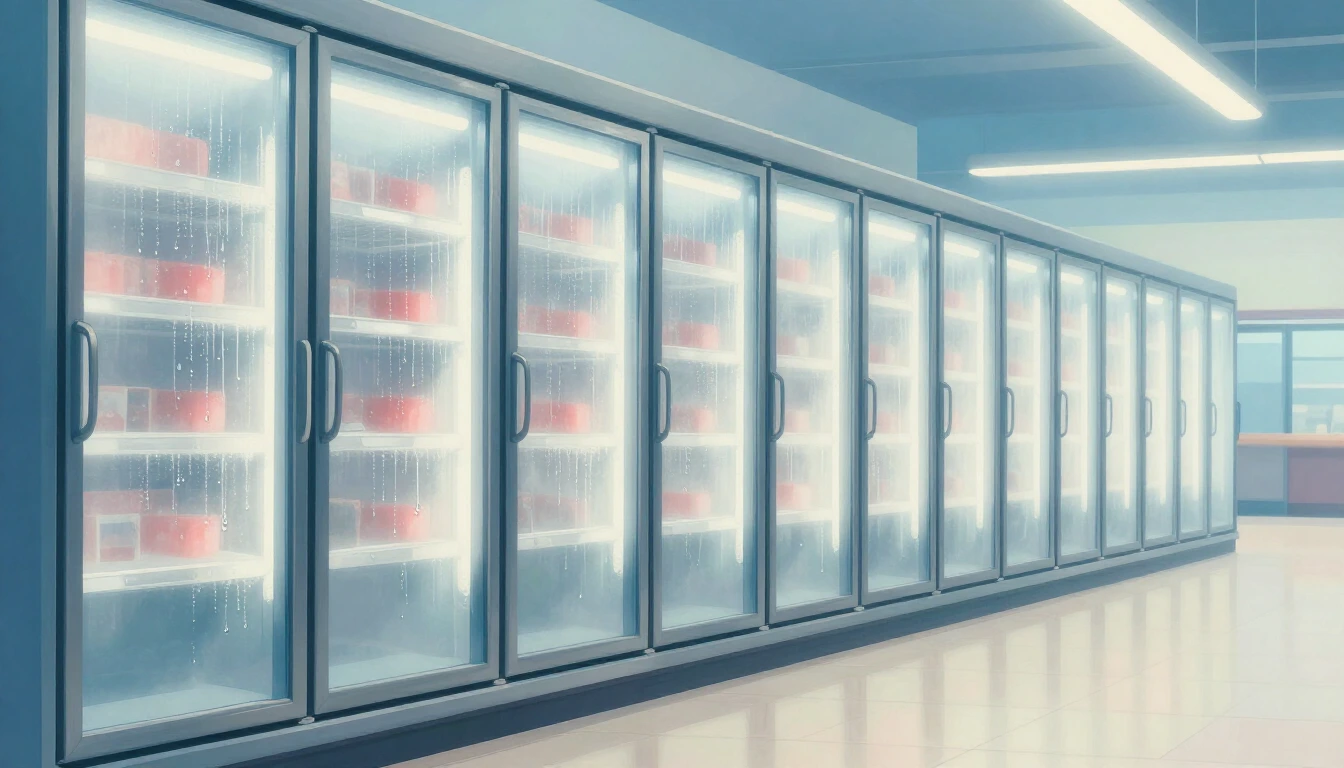
Around 4 a.m. on Monday, November 2, store managers at Ahold Delhaize in Belgium got a text message, according to the Belgian broadcaster RTL as cited by BleepingComputer. Something was wrong with the refrigeration. At the Delhaize in Eeklo, the freezers had been set to 50 °C, VRT NWS reported. In Sweden, ICA store manager Rickard Nilsson told the broadcaster TV4, as quoted by The Record: "We can’t adjust the temperatures, we can’t change them. Heat is blowing into the freezers. Everything is ruined." Nobody had broken in. Someone, somewhere, had reached the controllers that run the cold rooms and switched them into defrost.
That is the second time in three weeks. In the night of October 11 to 12, the same trick hit hundreds of supermarkets in France. Authorities published warnings. Manufacturers had shipped updates months before. And still, in the night of November 1 to 2, refrigeration systems in stores across at least six countries were switched into heating mode in a single night. Here is what is confirmed, what is only reported, and what nobody knows yet, because this story is easy to exaggerate.
Key takeaways
- More than 115 stores in at least six countries were hit in one night. BleepingComputer counts Belgium, the Netherlands, Sweden, Luxembourg, Ireland and Estonia; Finnish authorities and the retailer Kesko report problems in a few smaller stores in Finland as well.
- The method matches the French wave of October 11 to 12. The Belgian installer Sabcobel says evaporators were switched into defrost mode remotely, "exactly the same" mechanism as in France, where the Paris prosecutor’s office counts about 700 victims.
- The entry point was the internet. France’s CERT-FR warned on October 12 that remote management interfaces of refrigeration controllers were exposed online, against good practice, and that attack campaigns were "probably still ongoing."
- Nobody knows who did it. There is no attribution and no claim of responsibility. Belgium’s federal prosecutor has opened a criminal investigation, and Belgium’s cyber centre says the attacker may never be identified.
- Whether AI played any role is unknown. Belgium’s cyber centre warns about a general rise in attacks partly involving AI, but nobody has said AI was used in these attacks.
- Small, independently run stores were hit hardest. Chains report that affected stores sat outside their central networks or used their own older equipment. That is the lesson for every company with building technology online.
Products Worth Considering

LG UltraGear 32GX850A-B 32-inch 4K UHD Glossy OLED Gaming Monitor

DJI Mic 3 Wireless Microphone System (2 Transmitters, 1 Receiver, Charging Case)

Samsung 49-Inch Odyssey G93SC QD-OLED Curved Gaming Monitor
As an affiliate, we earn on qualifying purchases.
What happened in the night of November 1 to 2
In Belgium, Stephan Moelans, chief executive of the refrigeration installer Sabcobel, told RTL and Belga that his technicians were out from 1 a.m. disconnecting installations. He told Belgian media that Sabcobel itself was not hacked; the internet-reachable controllers in the stores were attacked directly. About 20 of the several hundred installations his company manages in Belgium were affected, he told The Record. According to VRT NWS, the butcher De Laet & Van Haver in Antwerp noticed the tampering around 3 a.m. and stopped its systems in time. Others were not so lucky. The Proxy Delhaize in Hoepertingen reported freezers at 15 °C instead of the usual minus 22 °C and estimated at least €60,000 of food thrown away, according to the regional paper Het Belang van Limburg as cited by VRT NWS. In Hove, a butcher’s shop put "hundreds of kilos" of food in the bin, VRT reported.
The companies confirmed the damage in their own words, to BleepingComputer:
- Ahold Delhaize: "We have identified an IT incident affecting the refrigeration systems in several dozen stores." BleepingComputer puts that at about 40 stores in Belgium and Luxembourg.
- Carrefour Belgium: "currently 15 of our 700 stores are affected, both in Flanders and Wallonia." "Not a single hypermarket is among them." It "only concerns a few refrigeration units, mainly freezers." A Carrefour spokesman told Euronews: "It’s a cyberattack, there is no other reason."
- Colruyt, on about five Spar stores: "These stores are operated by independent entrepreneurs who have their own refrigeration systems." Colruyt’s own stores were not affected, VRT reported.
- ICA in Sweden: at least four stores, "operating outside ICA’s central network."
- Coop in Sweden: 7 of more than 800 stores, with effects ranging "from completely shut-down refrigerators and freezers to partially functioning units" and "in one case, the system beginning to generate heat." Coop said: "The situation is currently contained and under control."
Add to that about 15 Intermarché outlets in Belgium, one IKEA store in Mons, 13 SuperValu stores in Ireland and one Selver store in Estonia. In the Netherlands, a Danfoss spokesperson told the Dutch broadcaster NOS that systems at "at least 17" businesses were hit, mostly butchers and neighbourhood shops. In Finland, Kesko’s head of security told Bloomberg that a few smaller K stores outside the group’s central safeguards had "temperature anomalies overnight," and Finland’s National Cyber Security Centre said the attacks there and elsewhere targeted specific Danfoss models, according to the Finnish news agency STT.
The numbers do not add up neatly, and that matters
BleepingComputer reports "over 115 stores in six countries." The Record reports more than 50 stores in Belgium alone. Euronews, citing the Belgian daily Le Soir, lists about 40 Delhaize Proxy, 15 Carrefour, 15 Intermarché and 5 Spar sites and arrives at 75 Belgian stores. VRT’s liveblog gives slightly different ranges. Temperatures also differ by store: 50 °C in Eeklo, Sweden and Estonia, 15 °C in Hoepertingen, 17 °C in Belgian units according to Euronews. Higher figures circulated in some media, but I could not confirm them, so I leave them out. Read every number in this story as "at least, as of Monday afternoon."
France was the warning shot
Three weeks earlier, the same thing happened at much larger scale. In the night of October 11 to 12, attackers "remotely defrosted refrigerators at multiple French supermarket chains overnight," BleepingComputer wrote. France 24, reporting with AFP, listed some 150 to 200 Intermarché shops, almost 100 Coopérative U outlets, 80 Carrefour supermarkets and around 30 Monoprix stores, with temperatures raised as high as 50 °C. E.Leclerc said "a cyberattack affected one of its refrigeration equipment suppliers," according to CBS News citing AFP. The Paris prosecutor opened an investigation into the "large-scale" attack, including fires, and later told The Record there were about 700 victims.
The response was quick and public. On October 12, CERT-FR, the French government’s computer emergency response team, issued alert CERTFR-2026-ALE-012 about "numerous compromises" of remote controllers for refrigeration installations. It names the Danfoss AK-SM and AK-SC series as well as Copeland and Dixell xweb devices; an update on October 13 added further targeted equipment. Danfoss said most affected units were "legacy" products that "no longer receive software or security updates," naming the AK-SM800 and AK-SC355, with some units running "outdated firmware," CBS News reported. On the day of the alert, the researcher Baptiste Robert of Predicta Lab counted 2,752 Danfoss systems reachable online, 1,590 of them in France, according to BleepingComputer.
So the second wave did not come out of nowhere. Finland’s cyber centre had warned its stores about two weeks earlier, when a few dozen of these devices were openly reachable from the internet in Finland, according to STT. Without that warning, the centre said, the situation could have been clearly worse. Danfoss put it plainly to NOS, as reported by VRT: most customers took measures after France, but a small number did not. "Die zijn nu de dupe," the spokesperson said. Those are now the ones paying for it.
Not the first time either
According to a Danfoss newsletter cited by The Record, attackers had already gone after controllers in Russian supermarkets when Russia invaded Ukraine, and 40 stores in Israel were hacked, which Danfoss said lacked adequate firewall or VPN protection. The same newsletter, The Record reported, announced a "hard End of Service" for older products, because continued support "would place Danfoss under new legal obligations to maintain security updates."
How the attack works, as far as anyone has said
Refrigerated cases regularly defrost: they warm the evaporator coils to melt ice. Store controllers schedule those cycles and are often reachable remotely so the contractor can monitor them. Force every unit into defrost and a freezer becomes a warm box. That is what Sabcobel describes.
What is not public is how the attackers got in. CERT-FR’s alert names no vulnerability, no indicators and no attacker. Its core point is about exposure: putting a management interface on the internet "est contraire aux bonnes pratiques," it is against good practice. Sabcobel’s Moelans says the same weakness as in France was used and that a software update alone is not enough; installations need physical changes. "That requires investment," he told Belga, as quoted by Euronews. "The simplest solution is to manage the fridges over a secure internet connection." Most of his customers switched to that after France, he said.
There are also known weaknesses on record. The US cybersecurity agency CISA published advisories in May and August 2025 for the Danfoss AK-SM 8xxA series: CVE-2025-41450, an authentication bypass, and CVE-2025-41451, a command injection flaw, both reported by researchers at Claroty Team82 and fixed in firmware releases R4.2 and R4.3.1. At the time, CISA said no public exploitation had been reported to it. Neither CERT-FR nor Danfoss has linked these flaws to the attacks in France or this week’s wave. They belong in this story as known weaknesses in the same product family, not as the explanation.
The ethical hacker Keanu Nys of Spotit told VRT NWS there is "geen enkele reden dat koelinstallaties openlijk toegankelijk zijn," no reason at all for refrigeration installations to be openly accessible. In his view, a known Danfoss weakness was used, and the patch from last year was not applied everywhere and only covered supported products. Asked who is behind it, he called that guesswork. He sees no financial motive and speculated it could be someone doing it for fun or a state trying to cause panic. That is his personal assessment, not a finding of any investigation.
Who is investigating, and what they say
Belgium’s federal prosecutor has opened a criminal investigation, confirmed to VRT NWS. The European Commission says it is coordinating with member states through CYCLONe, the EU network for cyber crises, which is run with ENISA, VRT reported.
Katrien Eggers, spokesperson for the Centre for Cybersecurity Belgium (CCB), told The Record: "It is not known who is behind this attack, and it may never be possible to identify them." The CCB is "concerned about the rising number of incidents, partly due to the targeted use of AI," which she described as "a development that has unfolded over the last six months." "We have recently seen a huge rise in the number of vulnerabilities where AI has been used to identify and exploit them," she said.
This is where headlines go wrong. That is a general warning about the threat landscape. Nobody, not the CCB, not CERT-FR, not the prosecutors, has said that AI was used in the refrigeration attacks. For these attacks, AI involvement is unknown. And no group has claimed either wave, The Record and Bloomberg report. Whether the October and November attacks were carried out by the same people is also unknown.
The US question
In the United States, Reuters reported on October 29 that the Pentagon is treating freezer failures at several military commissaries in late August as a suspected cyberattack, as summarised by The Next Web. Units "switched to defrost mode and warmed up, spoiling food." One official said investigators had talked with French police. But Reuters "could not establish whether the military commissaries used Danfoss equipment," and the Pentagon "has not confirmed that anyone gained access to the commissary systems." A connection to Europe is under investigation, not confirmed.
What this means for companies
The uncomfortable lesson is not about supermarkets. It is about every building with a controller on the network: refrigeration, heating and air conditioning, access control, lighting, pumps. This operational technology (OT) is often installed and maintained by a third party, bought to run for many years, rarely patched and almost never on the IT department’s inventory. In this wave, the chains say the hits landed where their central security did not reach: independent franchisees, stores "outside ICA’s central network," Spar stores with "their own refrigeration systems," Kesko’s smaller stores outside central safeguards.
CERT-FR’s alert reads like a to-do list, and I would use it as one:
- Take exposed units off the internet. Remove internet exposure of the controllers and of every unit on a public IP address. CERT-FR adds a practical warning: check your insurance contract before you cut the data feed to your refrigeration contractor.
- Check the whole configuration, "notamment les plages de dégivrage," especially the defrost schedules.
- Restore access only through a secure VPN or a protected network. Filtering by the contractor’s IP addresses on a firewall is acceptable in an emergency, CERT-FR says, but not as a lasting fix.
- Apply the manufacturer’s hardening. For Danfoss, that means updating firmware, setting the security level to "mode Strict" and making sure default passwords have been changed.
- Plan the replacement of end-of-life devices. For devices without security updates that stay exposed, CERT-FR warns that a factory reset alone "est dans ce cas insuffisant"; the device "sera certainement de nouveau compromis," it will almost certainly be compromised again.
Also ask your contractors, in writing, how they reach your equipment and whose accounts they use. And do not count on regulation to solve the old-device problem soon. The EU Cyber Resilience Act’s main obligations apply only from December 11, 2027, according to the European Commission. Until then, as The Record puts it, manufacturers have "no legal obligations" to fix the affected products. Your budget for replacing old controllers is your protection.
Hoepertingen alone estimated at least €60,000 in lost goods, Eeklo "tens of thousands of euros," per VRT. Weigh that against the cost of securing remote access before the next night.
What this means for shoppers
For most shoppers, the visible effect is empty freezer aisles and closed meat counters, VRT reported from Grembergen, Sint-Amandsberg and Ghent. The real loss falls on store owners, many of them independent entrepreneurs, who had to throw away stock.
Is the food on the shelf safe? Belgium’s food safety agency FAVV told stores they must check temperatures themselves, and products whose limits were exceeded may no longer be sold, as reported by VRT NWS. In Ireland, Musgrave pulled chilled and frozen goods at the 13 affected SuperValu sites as a precaution, Bloomberg reported. I could not find the FAVV guidance on its own website, so I am not quoting temperature limits here. The system is designed so that spoiled goods come off the shelf. As always, check use-by dates, and if frozen food looks thawed and refrozen, ask the store or leave it.
What we don’t know yet
- Who is behind it. No attribution, no claim of responsibility, no arrests reported as of Monday evening. Any talk of a state actor is speculation.
- Whether both waves have the same author. The method is the same, according to Sabcobel. Whether the actor is the same is unknown.
- How exactly they got in. Exposed interfaces are confirmed as the problem. Whether the attackers used a software flaw, default passwords or stolen maintenance accounts has not been officially stated.
- Whether AI played any role. The CCB warns about a general rise in attacks in which AI plays a part. For these attacks, that is unknown.
- The final count. Store numbers differ by outlet and keep moving.
- The US link. Whether the commissary failures in August are connected is under investigation, not confirmed.
The bottom line
The second wave of attacks on supermarket refrigeration did not need a new trick. It needed controllers that were still reachable from the internet three weeks after France rang the alarm. The big chains say their central networks held. The damage landed on independent stores and older equipment that nobody had moved behind a VPN.
That is the story worth telling, and it is less dramatic than "cyber war in the freezer aisle" and more useful. The fixes are known, public and cheap compared with the losses. If your company runs anything that heats, cools, opens or locks and has an IP address, now is a good week to find out who can reach it. If you want a parallel from IT, I wrote about why network edge boxes are attackers’ favorite door. The fridge is just the newest one.
Sources
- CERT-FR (ANSSI), "Incident de sécurité ciblant les contrôleurs à distance des installations de réfrigération", alert CERTFR-2026-ALE-012, October 12, 2026, updated October 13 and 16, 2026, cert.cyber.gouv.fr
- BleepingComputer, Bill Toulas, "Hackers disrupt refrigeration systems at European supermarkets", November 2, 2026, bleepingcomputer.com
- The Record by Recorded Future News, Alexander Martin, "Second wave of suspected cyberattacks hits supermarket freezers across Europe", November 2, 2026, therecord.media
- VRT NWS, liveblog "Federaal parket opent strafonderzoek na cyberaanval bij verschillende Belgische supermarkten", November 2, 2026, vrt.be
- Euronews, Jonathan Benton and Pascale Davies, "Cyberattacks hit supermarket fridges and freezers in Europe, Belgium launches investigation", November 2, 2026, euronews.com
- Bloomberg, Charlotte Hughes-Morgan and Christopher Jungstedt, "Supermarkets Across Europe Report New Suspected Freezer Hack", November 2, 2026, republished by Claims Journal, claimsjournal.com
- STT, "Kyberturvallisuuskeskus: Suomalaisyrityksiä varoitettiin jo pari viikkoa sitten, kun Ranskassa oli isketty kauppojen kylmälaitteisiin", November 2, 2026, via Satakunnan Kansa, sss.fi
- BleepingComputer, Sergiu Gatlan, "Cyberattack shuts down refrigerators at French supermarkets", October 12, 2026, bleepingcomputer.com
- France 24 with AFP, "’Unprecedented’ cyberattack targets refrigeration units at hundreds of French supermarkets", October 12, 2026, france24.com
- CBS News with AFP, "Hackers turn up the heat in refrigerators at hundreds of supermarkets in France, sparking fires and food losses", October 12, 2026, cbsnews.com
- CISA, "Danfoss AK-SM 8xxA Series (Update A)", ICS advisory ICSA-25-140-03, May 20, 2025, updated August 26, 2025, cisa.gov
- The Next Web, Ana-Maria Stanciuc, "Pentagon suspects hackers behind freezer failures at US base stores", summarising a Reuters report, October 29, 2026, thenextweb.com
- European Commission, "Cyber Resilience Act", policy page, retrieved November 2, 2026, digital-strategy.ec.europa.eu
This article is for information only. It is not legal, security-consulting or insurance advice. If you run affected equipment, follow CERT-FR’s guidance and talk to your refrigeration contractor and insurer.