By Thorsten Meyer | November 10, 2026 | ThorstenMeyerAI.com

Get business pricing on tech for your team
- Business-only prices and quantity discounts
- Tax-exempt purchasing
- Multiple users, one account, clear invoices
Update, November 11, 2026, 07:18 UTC: N-able has released N-central 2026.4 HF2 (build 2026.4.1.26). Its release notes are dated November 10, with a publication timestamp of 20:48 UTC. According to N-able’s status page, all hosted N-central servers had been upgraded by 01:04 UTC on November 11. N-able “strongly recommends” that on-premises customers upgrade “as soon as possible” and says a “follow-up hotfix will be released to provide further security updates”. Seven CVEs are now published. Details in the hotfix section below.
Key takeaways
- What happened: On Monday, November 9, 2026, N-able took its hosted N-central environments offline and told customers who run N-central on their own servers to switch them off too. The trigger: a researcher published more than 30 alleged security flaws, with attack code, late on Sunday.
- Why it matters: N-central is a remote monitoring and management (RMM) tool. IT service providers use it to run the computers of many client companies from one console. A hole in that console is a door into every network behind it.
- N-able’s position: It calls the release a “non-responsible communication of critical vulnerabilities”. It says it sees “scanning activity associated with the published proof-of-concept code” but has “no evidence that any customer environment has been successfully exploited.”
- The fix: N-able has released N-central 2026.4 HF2. Its status page says it addresses “the most critical November 9 vulnerabilities” and that “a follow-up hotfix will be released”. By 01:04 UTC on November 11, all hosted servers had been upgraded, according to N-able. On-premises servers need their own upgrade.
- What is not known: whether all the flaws are real, how the seven published CVEs map to the more than 30 flaws the researcher released, whether anyone got in before the shutdown, and what the follow-up hotfix will cover.
Products Worth Considering

Bose TV Speaker Compact Soundbar with Bluetooth and HDMI-ARC, Black

LG UltraGear 32GX850A-B 32-inch 4K UHD OLED Gaming Monitor

Samsung Galaxy Tab A11+ 8GB RAM, 256GB Storage, Gray
As an affiliate, we earn on qualifying purchases.
A Sunday-night release, a Monday shutdown
Most security flaws reach the public after the vendor has had time to fix them. This time it went the other way.
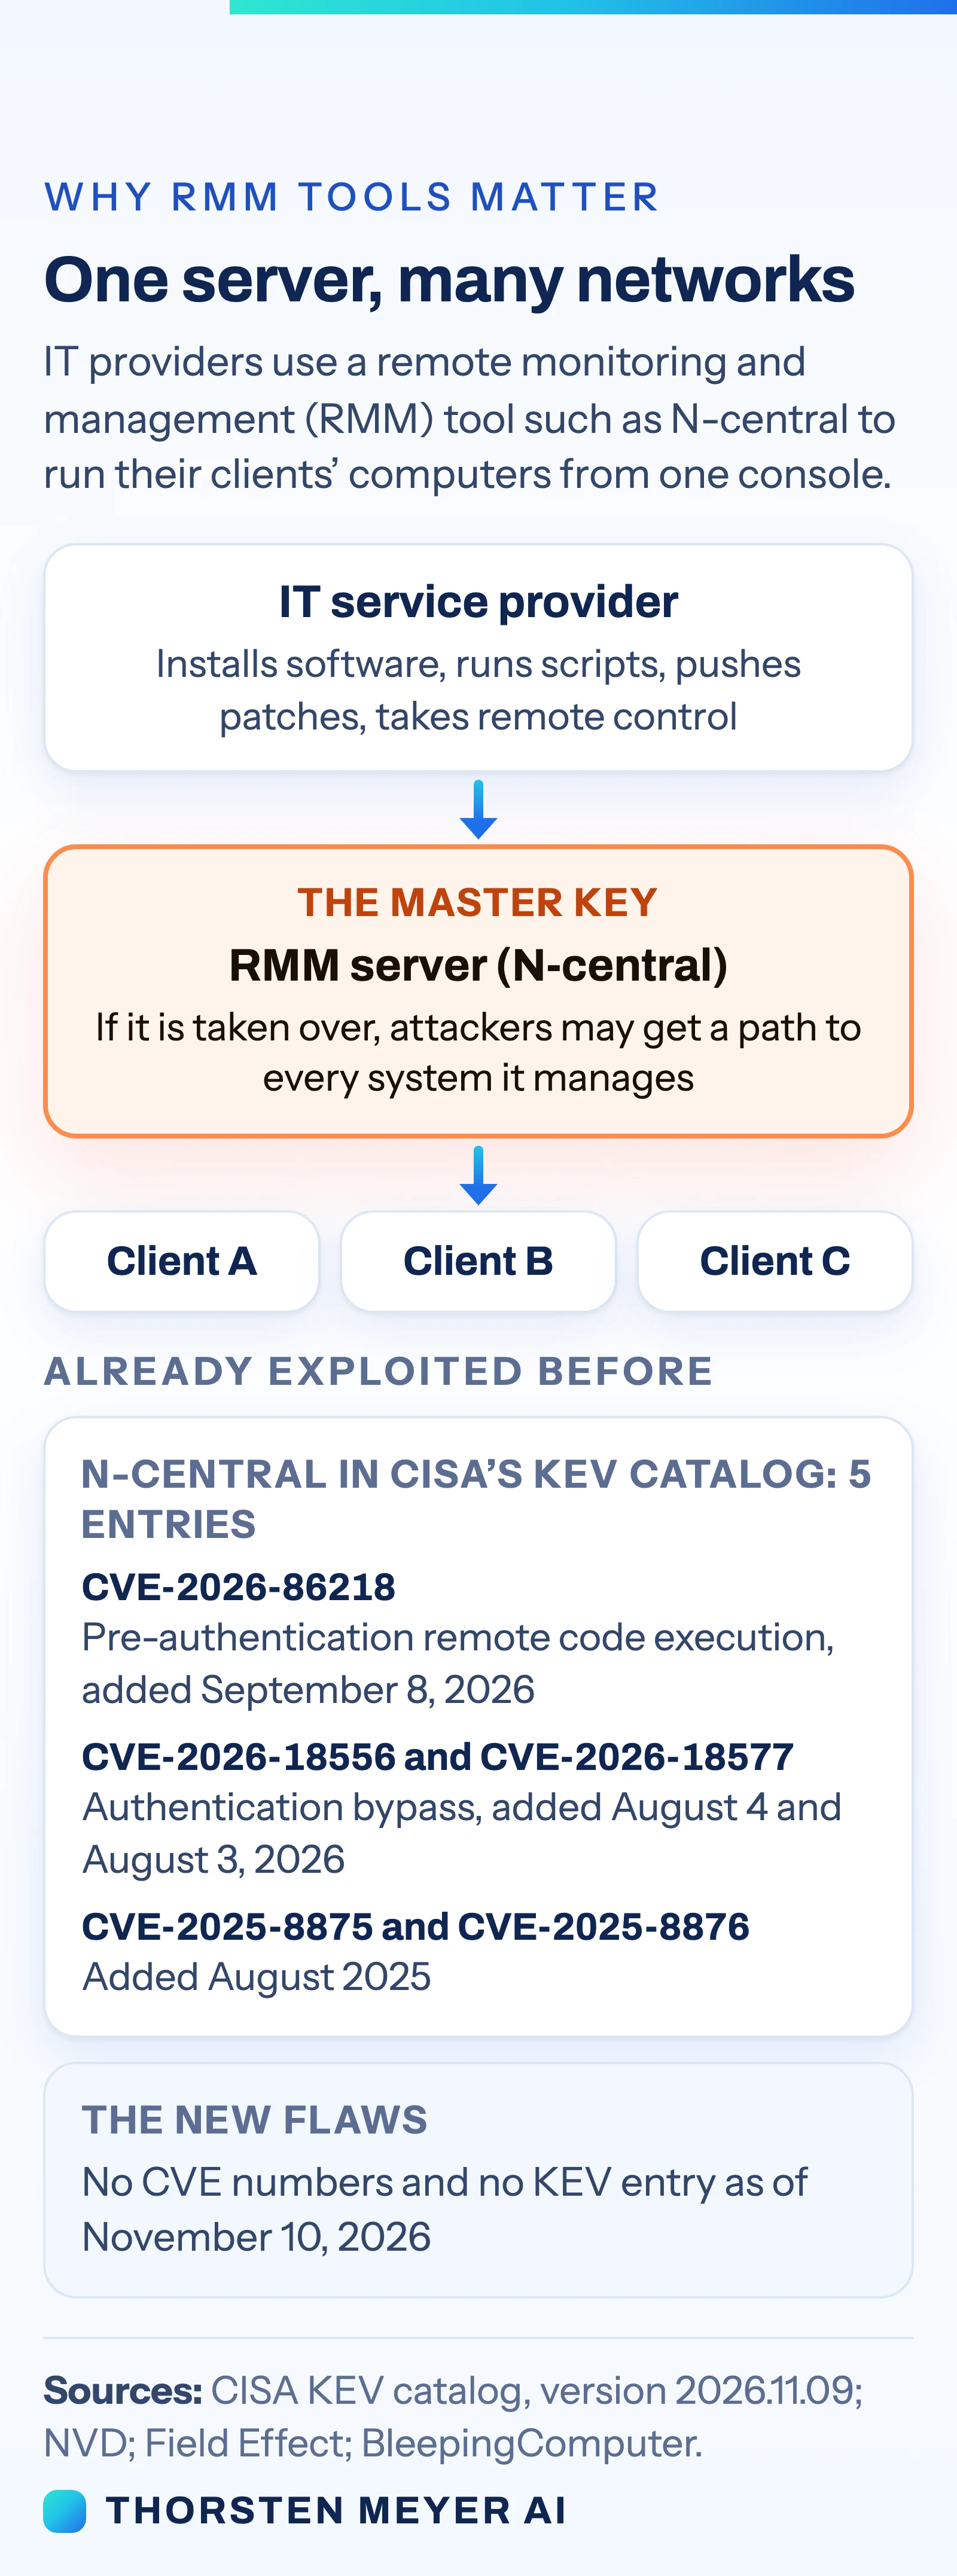
According to BleepingComputer, a security researcher published a GitHub repository called Able2Shell “late Sunday, November 8”, with proof-of-concept exploits for more than 30 flaws in N-able’s N-central. The Hacker News puts the number at 33. N-able had no fix ready. On Monday, it pulled the plug.
“As a precautionary measure, we have temporarily taken our Hosted N-central environments offline while we take the necessary actions to secure the environments and implement appropriate remediation,” N-able writes on its status page. Customers “will be unable to access their Hosted N-central classic environment, and associated services may be unavailable.”
For customers who run N-central themselves, the advice is just as drastic. N-able “strongly advises customers operating On-Premises N-central servers to temporarily take their N-central servers offline and keep them offline until N-able provides further guidance confirming they can safely be brought back online.”
The status page lists the incident as a “Major Outage” for hosted and on-premises N-central in the Americas, APAC and Europe.
Why an RMM server is a master key
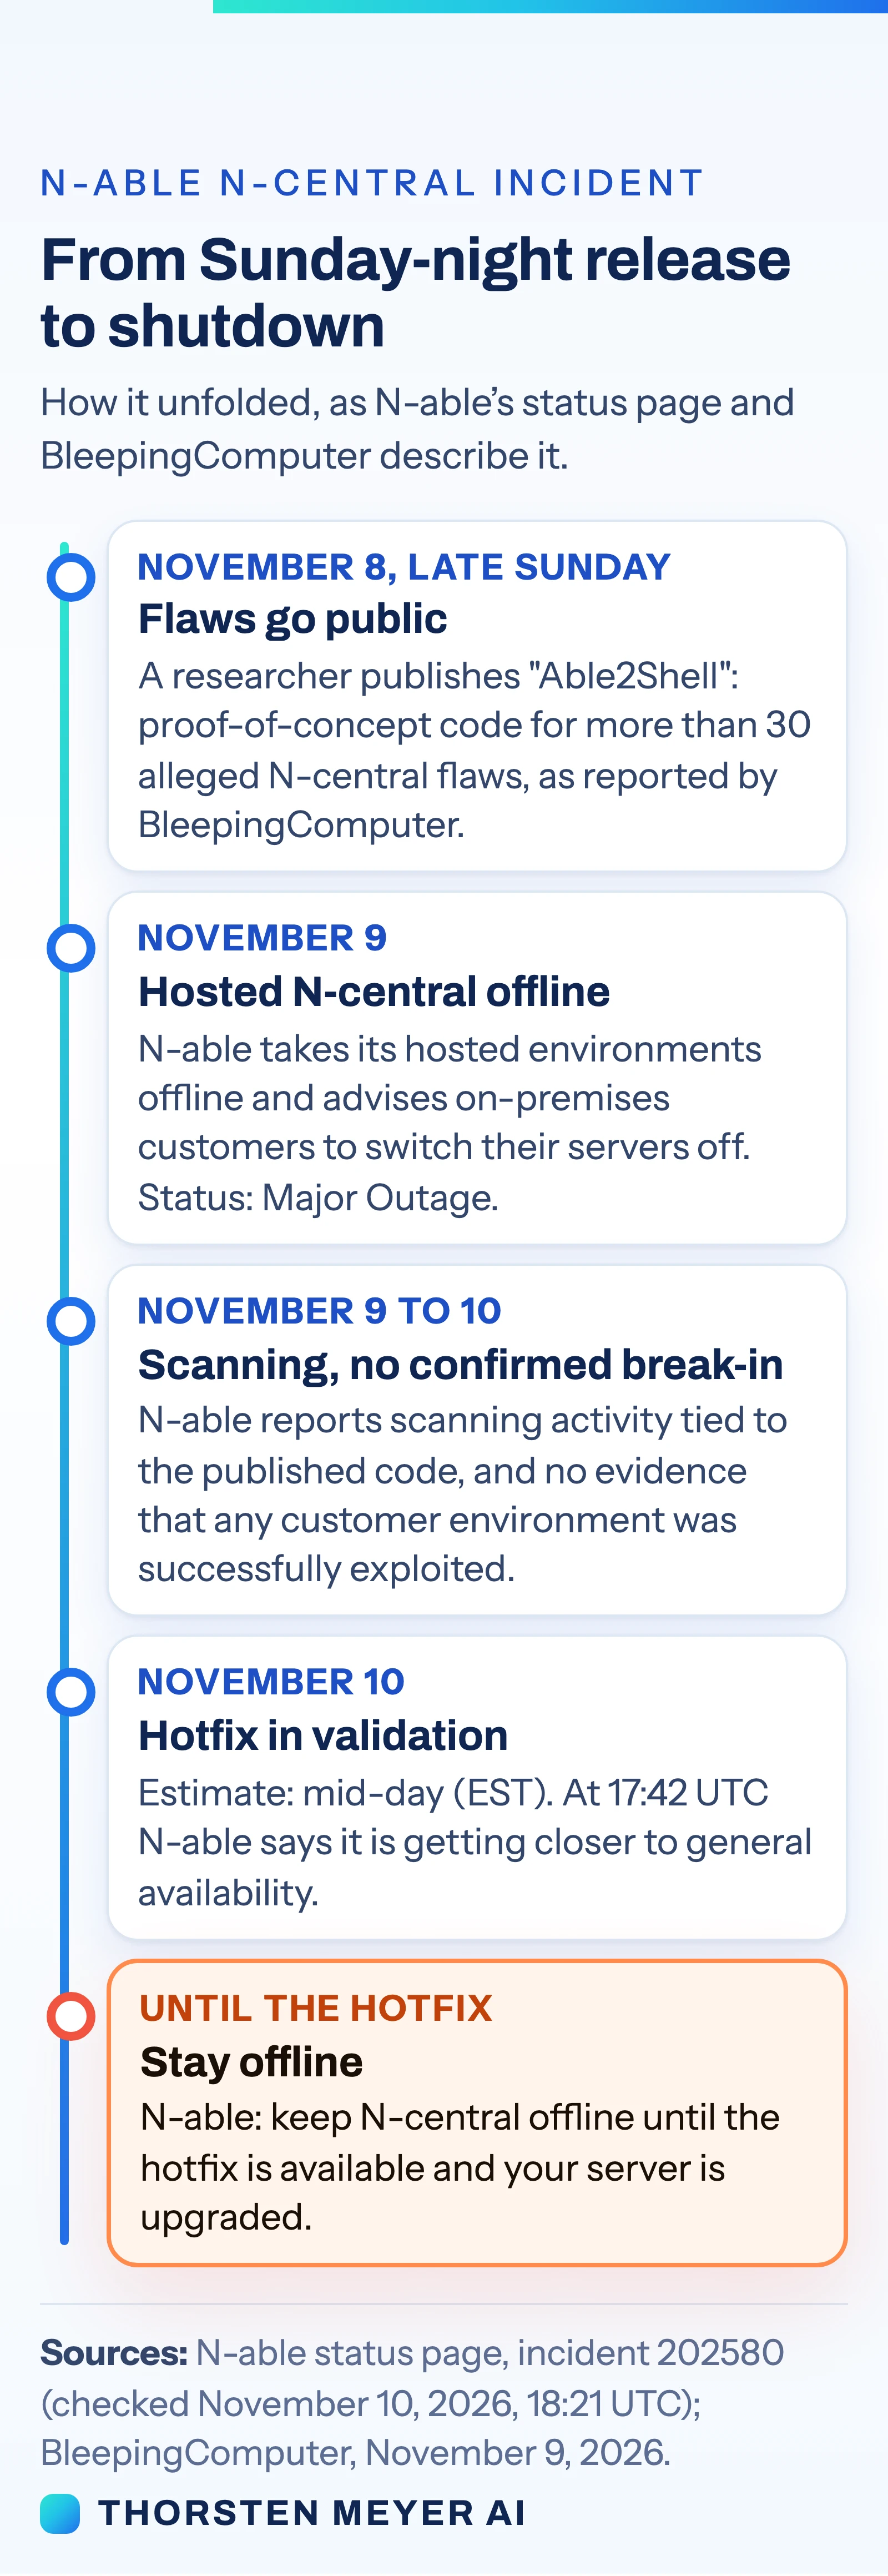
To see why N-able reacted this hard, you need to know what N-central does. BleepingComputer describes it as a platform “used by managed service providers (MSPs) and IT teams to monitor, manage, and secure customer devices and networks remotely.”
In plain words: if your company pays an IT provider to look after its computers, that provider may use a tool like N-central. From one screen, it can install software, run scripts, push patches and take remote control of your machines, and of the machines of its other clients.
That makes the server running the tool a master key. The security firm Field Effect puts it this way: “a compromised N-central server can give attackers a path to downstream systems.” One break-in at the provider can become a break-in at many customers.
This is not a theoretical worry for N-central. CISA, the US cybersecurity agency, keeps a catalog of Known Exploited Vulnerabilities (KEV), flaws that attackers have actually used. In the catalog version of November 9 that I checked, N-able’s N-central has five entries. Three were added this year: CVE-2026-18577 and CVE-2026-18556, two authentication bypass flaws added on August 3 and August 4, and CVE-2026-86218, a flaw CISA says “could allow for pre-authentication remote code execution”, added on September 8. CISA notes that CVE-2026-18577 “is the result of an incomplete patch for CVE-2026-18556.” The two older entries, CVE-2025-8875 and CVE-2025-8876, date from August 2025.
What the researcher published, and what N-able says
BleepingComputer and SecurityWeek name the researcher as Sean Bales. BleepingComputer reports that the flaws were tested against “N-central Appliance 2026.4.0.31, a pre-release version of the software”, and that the researcher “believes most, if not all, flaws also affect earlier versions.” He also told BleepingComputer that the discovery “was AI-assisted.”
The flaw types BleepingComputer lists include authentication bypasses, credential disclosure, cross-site scripting and “remote code execution (RCE) flaws”. In plain words: ways to get past the login, to steal passwords, and to run commands on the server. I will not go into the exploit details here.
Why publish without warning? The researcher told BleepingComputer that N-able had not fixed other flaws he had reported earlier in a different N-able product: “These have yet to be patched. I did not disclose any of the 0-days I posted last night.” BleepingComputer says N-able did not address those claims and sent only its statement on the incident.
That statement is sharp about how the flaws came out. “N-able is actively responding to non-responsible communication of critical vulnerabilities in N-central late Sunday night, November 8, found by an independent researcher,” the company told BleepingComputer. In its status page and its statement, N-able does not call the flaws “zero-days”, and it has not confirmed the count. BleepingComputer writes that it has “not independently verified all the reported vulnerabilities”, but that N-able’s hotfix work lends “credence” to the claim that at least some are real.
Two other signals came from outside. The security firm watchTowr said in a post on X, quoted by The Hacker News, that it “observed exploitation attempts against N-able N-central honeypots overnight”. Honeypots are decoy servers set up to attract attackers. And N-able itself says: “As expected, we are observing scanning activity associated with the published proof-of-concept code.”
As of my checks on November 10, the flaws had no CVE numbers. NVD, the US vulnerability database, had no N-central entry published since October 1, and none of the new flaws were in CISA’s KEV catalog. SecurityWeek also reports that they “have yet to be assigned CVE identifiers.” That changed late on November 10, when N-able published seven CVEs with its fix (see below).
How many servers could be exposed? Censys, a company that scans the internet, wrote in its November 9 advisory that a search of its platform “Found: 1,728 hosts” running N-central. That is a count of servers it could see, not of servers proven vulnerable or attacked. Here are the key numbers so far, each with its source:

The hotfix is out
N-able released N-central 2026.4 HF2 late on November 10. Its release notes are dated November 10, and the page carries a publication timestamp of 20:48 UTC. They describe “a critical security update” and list build 2026.4.1.26.
On its status page, N-able writes: “The N-central release addressing the most critical November 9 vulnerabilities is now available.” It adds: “Please note that a follow-up hotfix will be released to provide further security updates as part of our ongoing response to the disclosure.” HF2 is not the last word.
For hosted customers, N-able’s status page reported at 01:04 UTC on November 11: “All Hosted N-central servers (NCODs) across all global regions have been successfully upgraded.”
For on-premises customers, “N-able strongly recommends that all N-central On-Premises customers upgrade to the newly released version as soon as possible.” Until then, its advice stands: “We continue to recommend that N-central servers remain offline until your server has been successfully upgraded.”
Two more points from the release notes matter for IT providers. “All customers, both hosted and on-premises, must upgrade their Agents and Probes”, the N-central components that run on and near managed machines. And “Built-in remote control is temporarily disabled”, while “Take Control continues to work as expected.”
N-able lists seven CVEs as fixed in HF2, with these titles:
- CVE-2026-125883: “Multiple XXE Vulnerabilities”
- CVE-2026-125878: “Multiple OGNL Injection vulnerabilities”
- CVE-2026-125879: “Local privilege escalation to root via nable-writable syslog-ng config”
- CVE-2026-125880: “Stored XSS via MMS3 patch metadata (admin context)”
- CVE-2026-125881: “Schema-hint SSRF via service import schema validation”
- CVE-2026-125882: “RCE via file repository upload path traversal”
- CVE-2026-91000: “Insecure IPC Channels lead to local privilege escalation”
The researcher’s release counted more than 30 flaws, and The Hacker News put the number at 33. N-able has not said how its seven CVEs map to that list. NVD received all seven records late on November 10, between 22:18 UTC and 22:21 UTC. They carry CVSS 4.0 scores between 8.3 and 9.3 from the organization that submitted them, and NVD had not yet analyzed them. None of the seven was in CISA’s KEV catalog version of November 10. N-able also says it is still “observing scanning activity associated with the published proof-of-concept code.”
On a clock, using the times on N-able’s status page, about 35 hours passed between the incident start and N-able’s notice that all hosted servers were upgraded:

During the outage, some N-able services kept running. The company said “Ecoverse services available through N-able Login remain online, including Asset View, Patching, Vulnerability Management, scripting, policies, and tagging.”
What this means for businesses
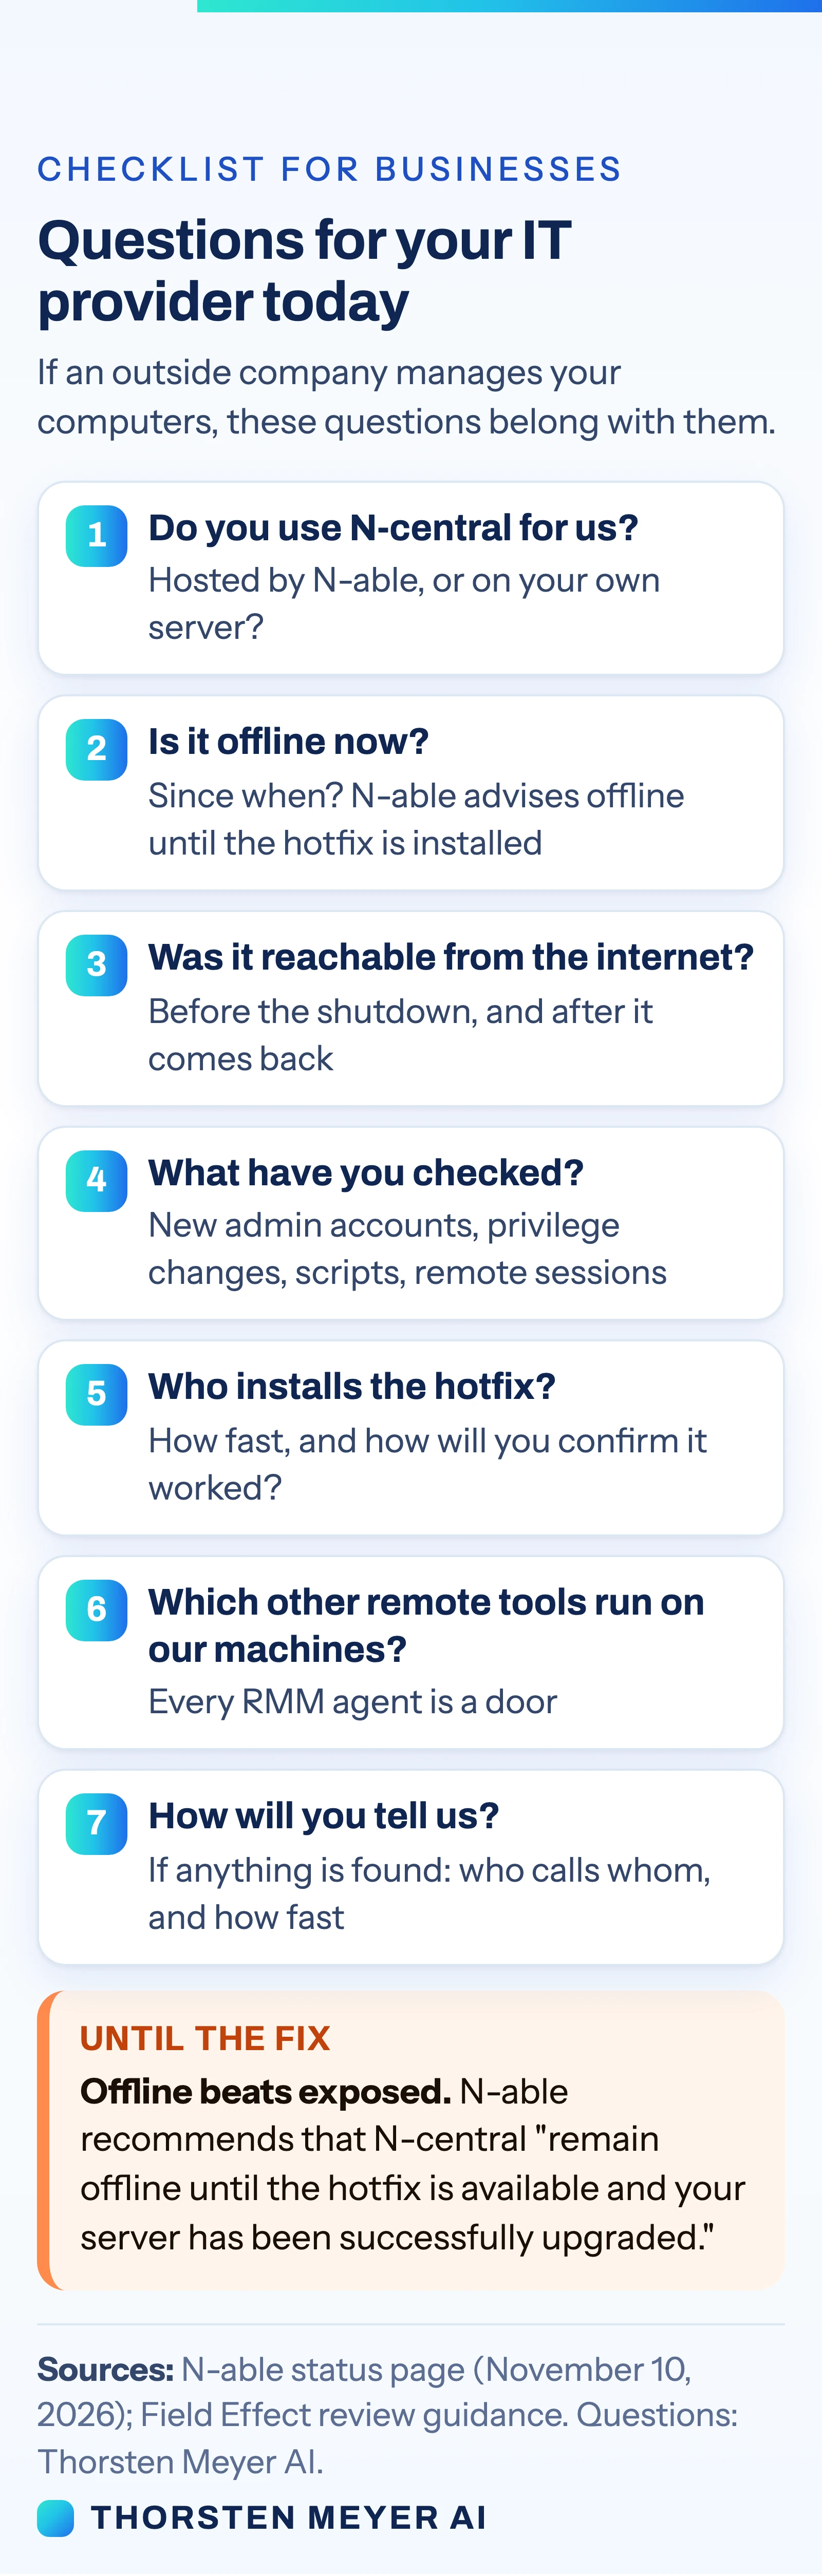
Most companies affected by this will never log in to N-central themselves. Their IT provider does. So the questions belong with that provider. Here is what I would ask today:
- Do you use N-central for our systems? If yes, hosted by N-able or on your own server?
- If on your own server: is it offline now, and since when? N-able advises keeping it offline until the hotfix is installed.
- Could anyone reach it from the internet before that? Field Effect advises checking whether “N-central management interfaces are accessible from the public internet.”
- What have you checked? Field Effect advises reviewing “administrator account creation, privilege changes, configuration modifications, software deployments, script execution, remote-control sessions, and automation policy changes”, with “particular attention to activity immediately before systems were taken offline.”
- Have you installed the hotfix? N-central 2026.4 HF2 is out. When was our server upgraded, were the Agents and Probes updated as N-able’s release notes require, and how did you confirm it worked?
- Which other remote tools are on our machines? Every RMM agent is a door. You should know which ones are installed and who holds the keys.
- How will you tell us if something was found? Agree on who calls whom, and how fast.
Longer term, treat your IT provider’s tools as part of your own attack surface. Ask for the same things you would ask of any critical supplier: which tools they use, how they protect admin access, how fast they patch, and how they would tell you about an incident. Make sure the answers are in your contract.
If your own IT team runs N-central, follow N-able’s release notes and status page: N-able advises keeping the server offline until it is upgraded to HF2, and says Agents and Probes must be upgraded too. Where you find unauthorized activity, Field Effect advises rotating “credentials associated with N-central administration, service accounts, and integrations.”
What this means for users
If you work at a company that uses an outside IT provider, you may notice slower support this week, or remote help that does not work. N-able says hosted N-central servers have been upgraded, but providers who run their own servers have to upgrade them first, and N-able says its built-in remote control is temporarily disabled.
Be careful with unexpected calls, emails or chat messages from someone claiming to be IT support that ask you to install a tool, approve a remote session or share a code. Confirm through a number or channel you already know. There is no published sign of such tricks in this case, but outages are a common pretext.
What we don’t know
- Whether all the flaws are real. N-able has not confirmed the count or the details. BleepingComputer has not verified all of them.
- Which versions are affected. The researcher tested a pre-release version, according to BleepingComputer. N-able’s fixed build is 2026.4.1.26, but it has not published a full list of affected versions.
- Whether anyone got in. On November 10, N-able said it had “no evidence” of successful exploitation. TechCrunch reports that an N-able spokesperson did not answer whether the company has the means to check.
- How much HF2 covers. N-able lists seven CVEs and announces a follow-up hotfix. It has not said which of the researcher’s flaws remain open.
- What happened with the earlier reports. The researcher says flaws he reported months ago in another N-able product are still open. N-able has not responded to that publicly.
- How many companies are affected. Neither N-able nor any source I found gives a number of providers or client networks.
The bottom line
N-able made a hard call: switch off a tool its customers rely on every day, rather than leave it exposed to published attack code. That costs a lot of IT providers a difficult week. But it also shows the problem with remote management tools in plain sight. They are built to reach everything, which is exactly what makes them dangerous when they break. If an outside company runs your IT, its tools are part of your security, and you have every right to ask about them.
For more context, read why AI has taken the clock off cyberattacks, how Rhysida got into Berlin’s administration, and what to do after this autumn’s firewall fixes and stolen tokens.
I’m Thorsten Meyer. The full sources are below, and more reality checks are at thorstenmeyerai.com.
Sources
- N-able: status page, “IMPORTANT: N-central Critical Security Incident”, incident 202580, uptime.n-able.com, checked November 10, 2026 at 18:21 UTC, 18:28 UTC, 19:27 UTC and 19:37 UTC (latest entry 17:42 UTC)
- N-able: status page, “N-central Critical Security Incident – Release Available”, incident 202584, uptime.n-able.com, checked November 11, 2026 at 07:18 UTC
- N-able: “N-central 2026.4 HF2 Release Notes”, status.n-able.com, November 10, 2026
- N-able: statement to BleepingComputer, November 9, 2026
- CISA: Known Exploited Vulnerabilities catalog, versions 2026.11.09 and 2026.11.10, cisa.gov
- NVD (nvd.nist.gov): no N-central CVE published between October 1 and November 10, 2026, before the fix; records for the seven HF2 CVEs received on November 10, 2026
- BleepingComputer, Lawrence Abrams: N-able takes cloud platform offline after 30+ “zero-days” published (November 9, 2026)
- The Hacker News: “N-able Takes N-central Cloud Offline After Researcher Discloses 33 Zero-Days with PoC Exploits”, November 10, 2026
- SecurityWeek: “N-able Takes N-central Offline as Researcher Drops Over 30 Zero-Days”, November 10, 2026
- TechCrunch: “N-able takes its remote access service offline after researcher publishes dozens of zero-day bugs”, November 10, 2026
- Field Effect: “N-able takes N-central offline as alleged zero-day exploits surface”, fieldeffect.com
- Censys: “Nov 9 Advisory: N-able N-central Multiple Critical Vulnerabilities, Publicly Disclosed”, November 9, 2026, censys.com (host count from its platform search)
Researched and drafted with AI assistance, including Anthropic’s Claude. No company or agency named here reviewed or sponsored this article. This article is for information only. It is not legal or security-consulting advice. Statements as published by N-able and the sources above as of November 11, 2026, 07:18 UTC; check N-able’s status page for later updates. Images: AI-generated illustration (Runware) and graphics by Thorsten Meyer AI; no real people or logos are shown.